Currently, agents need permission to access the Journey itself in order to see Journey information referenced on a ticket.
I think visibility should instead be based on the agent’s permission to view the ticket. If an agent has access to a ticket, they should also be able to see the Journey information associated with that ticket, without requiring separate access to the Journey or its primary workspace.
View of business agent that has access to the journey ticket and access to the journey in the primary workspace:
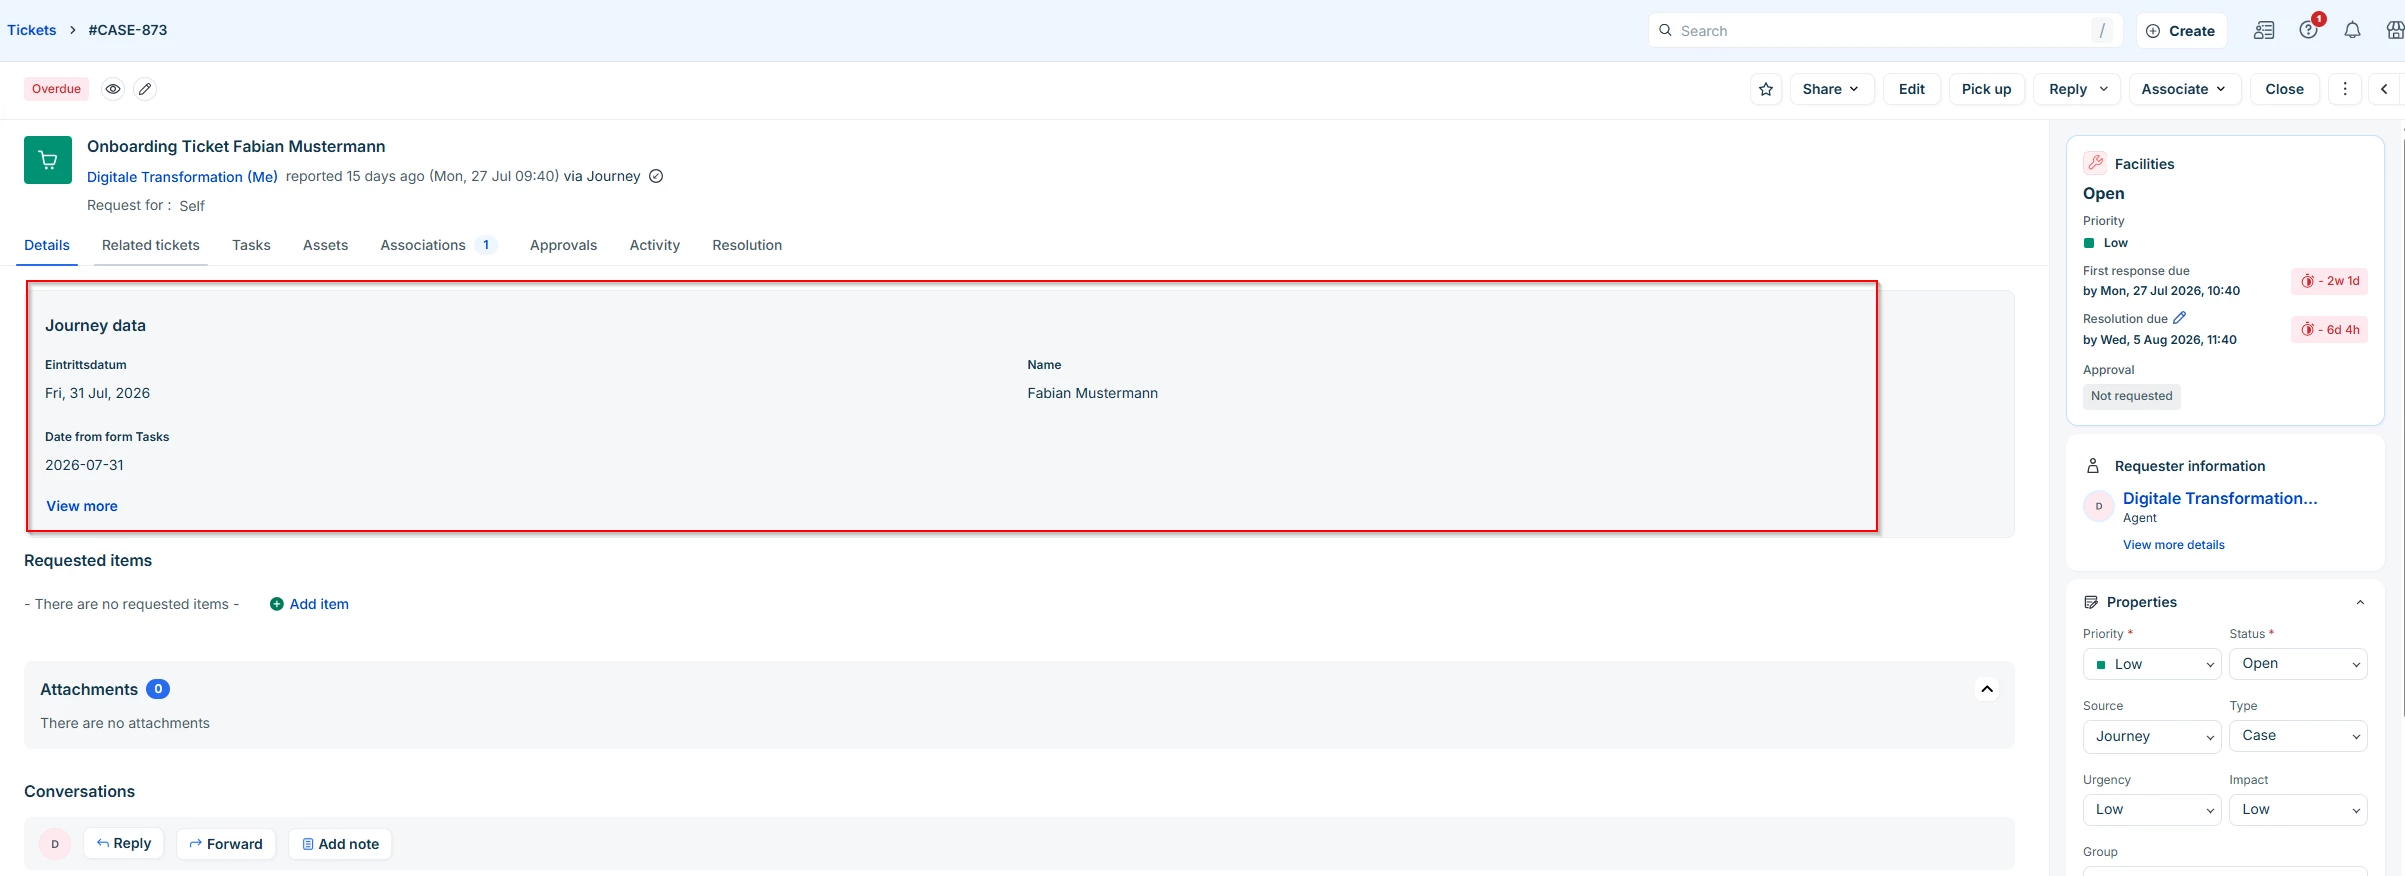
View of business agent that only has access to the journey ticket (but not access to the journey in the primary workspace):
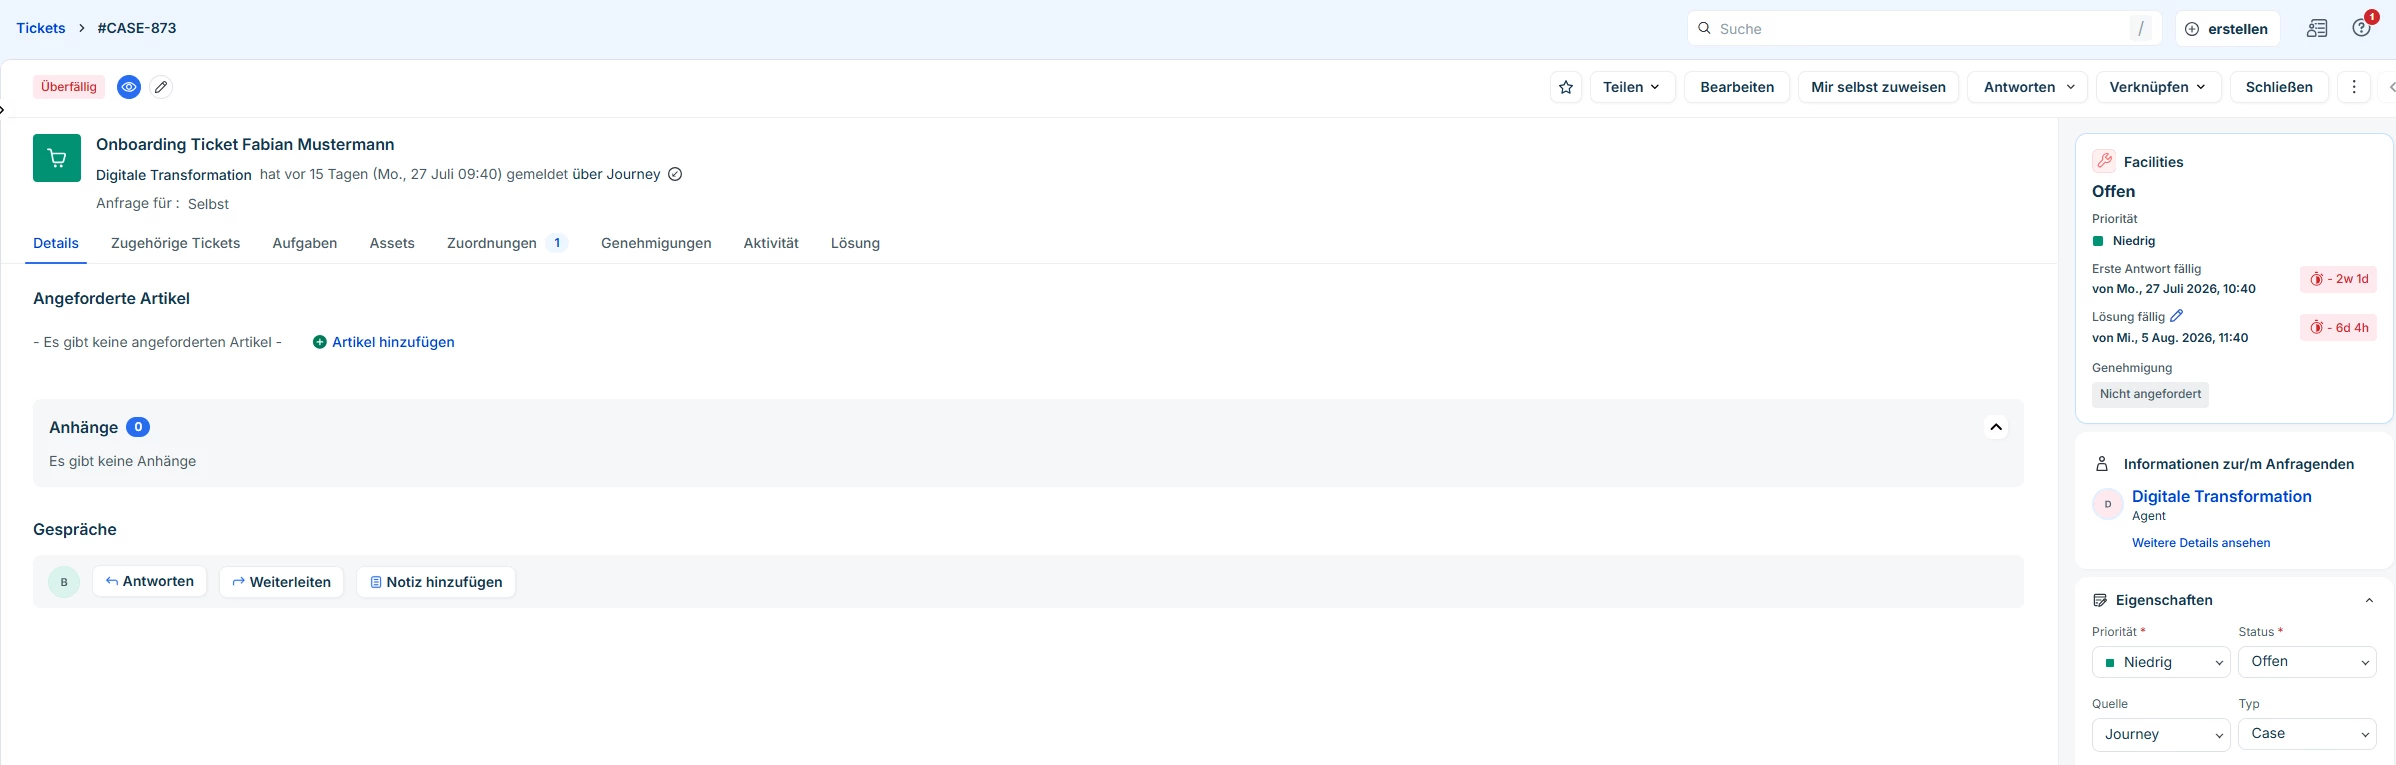
A typical use case:
A Journey request is managed within the IT workspace or by a specific group. As part of the Journey, individual task tickets are created and assigned to other groups or workspaces.
Agents in those groups have access to their assigned tickets, but they may not have access to the original Journey in the IT workspace. As a result, they cannot see the Journey information shown on their tickets, even though that information is relevant to completing their tasks.
The same issue applies to files attached to Journey tickets: an agent may have permission to work on the ticket but still be unable to access the associated files because they do not have permission to access the Journey itself.
Suggested behavior:
If an agent has permission to view a ticket, they should also be able to view the Journey information and access files made available through that ticket. Access to the complete Journey itself could remain controlled by the existing Journey/workspace permissions.
This would make cross-workspace and cross-group Journeys much easier to use while still keeping access to the full Journey appropriately restricted.